Argos case study: the first NEXTAI agent with a digital ID
What Argos does, what it is forbidden to do, what its A4 level means and how to check its credential in 30 seconds without signing up anywhere.
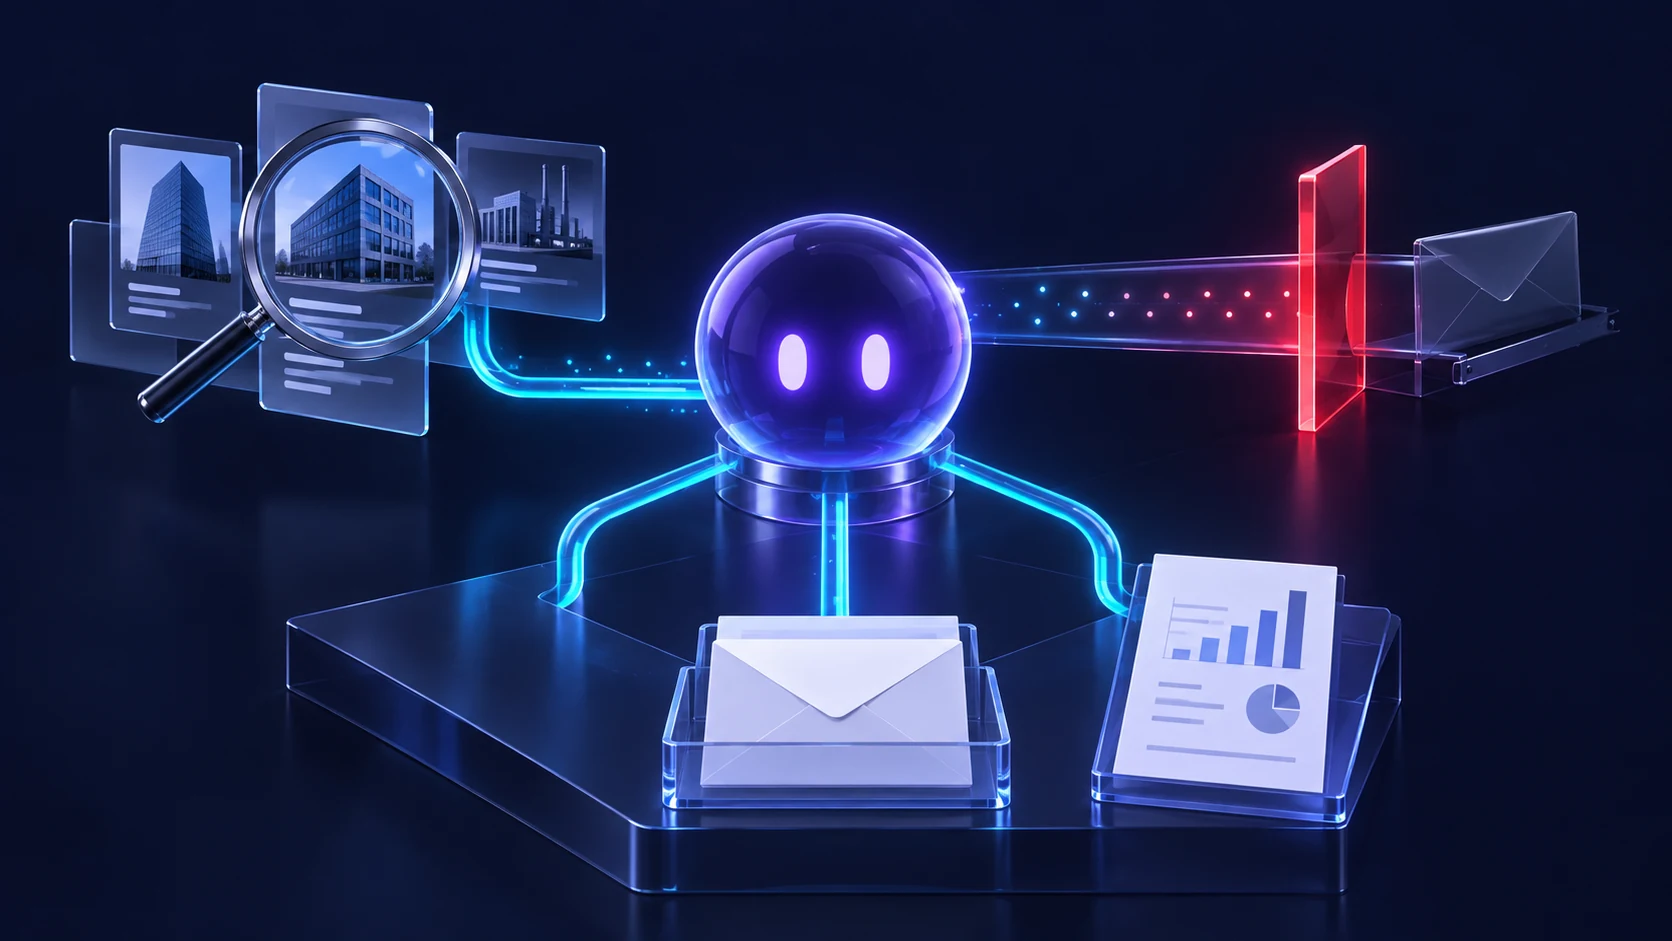

Argos is the NEXTAI prospecting agent, known internally as "Lead NEXTAI", and the first of our agents with a verifiable digital identity: credential CRD-2026-0001, issued on 8 September 2026, maximum autonomy level A4 and low risk. What matters about the case is not what Argos can do, but that what it cannot do is written down, signed and published, and anyone can check it.
What Argos does
Argos works at the top of the commercial funnel. It scouts potential clients, qualifies them against defined criteria, researches their public context, drafts outreach messages and produces status reports for the team.
So far, nothing remarkable: that is what many commercial agents on the market do. The difference is in the boundary.
What it cannot do
| Declared scope | Prohibitions in the credential |
|---|---|
| Scout leads | Send communications (outreach.send) |
| Qualify leads | Execute payments |
| Research public context | Sign contracts |
| Draft outreach | Delete data |
| Produce status reports | Modify other agents |
The reference credential authorises drafts and forbids outreach.send, payments, contracts, deletion and the modification of agents. A4 does not cancel those prohibitions. This document describes the signed scope; it does not attest to the behaviour of every commercial process and it is not proof of a block in each connector.
Scope and prohibitions are signed fields of the credential. Changing them in the document without signing again invalidates the signature. The manifest hash is a separate reference; it does not imply that any external permission change is detected automatically.
What the A4 level means
Our autonomy scale has five operational levels and a boundary:
| Level | Name | What it allows |
|---|---|---|
| A0 | Observe | Read, search, measure |
| A1 | Analyse | Classify, summarise, estimate |
| A2 | Prepare | Drafts, proposals, plans |
| A3 | Execute internally | Reversible internal changes |
| A4 | Execute with approval | Persistent or external action only with valid human approval |
| A5 | — | Not a reachable level: it is the class of actions forbidden to any agent |
The credential declares a maximum level of A4. Within the CORTEX scale, authorised external actions require approval; outreach.send remains forbidden in this credential. Enforcing these rules effectively needs additional controls and tests.
A0–A5 is an internal CORTEX scale. A4 is a ceiling, not a universal authorisation: an expressly forbidden action stays forbidden even if someone approves it. Its effective enforcement depends on the execution controls.
Before widening a commercial agent's remit, ask for evidence of the permission, of the rejection outside scope, and of access withdrawal.
How to check it in 30 seconds
There is no need to sign up, install anything or ask our permission.
- Open the public Argos verifier, or scan the QR code on the seal with your phone camera.
- Watch the eight checks running live: credential format, the key declared by the issuer, signature, issuer consistency, validity, revocation, unchanged manifest and published DID document.
- Read the transparency notice, which identifies Argos as an artificial intelligence system operated by Cosmolabs OÜ and makes clear it is not a person.
- Review the issuer: Cosmolabs OÜ, an Estonian company with registry code 17106582, and its DID document published at
did:web:digitalcortex.tech. - Look at the scope block: what the credential attests and what it does not.
- Cross-check with the registry: the public agent registry returns the list in JSON, with each agent's current status.
The practical rule: if any of the eight checks fails, do not trust it. And on the seal itself, the colour sums up the permissions at a glance. Light diamonds, what is permitted; red diamonds, what is forbidden. The more red diamonds, the more tightly bounded the agent — which in security is good news.
If the credential expires or is revoked, the verifier and the served seal should reflect that according to their refresh behaviour and caches. A screenshot can preserve an old state. The revocation and cut-off guide distinguishes public status from the effective withdrawal of permissions.
What would happen if we widened its permissions
Widening what Argos can do requires an explicit change of authorisation. Its reference credential forbids outreach.send: an A4 approval does not enable that send.
The credential binds an identity declaration to the hash of the registered manifest. The scope is signed at issuance. To detect a change of prompt, model or permissions outside that registry you have to check the effective configuration: the hash does not automatically observe external systems. Every approved change of scope requires reviewing and reissuing the declaration.
Personal data: what it contains and what it does not
Argos's credential contains no personal data about individuals. The responsible party is the company, Cosmolabs OÜ, with an accountable role and a legal contact address. There are no employee names, no personal identifiers and no information about the leads Argos works with.
That is a design decision: an agent's identity should say who is institutionally accountable, not expose whoever configured it.
Why we started with the commercial agent
Because it is the one that talks to people outside. An internal agent that files documents raises operational risks; an agent that writes to potential clients also raises a transparency question: the person on the other side has a right to know they are talking to a system and who answers for it.
Article 50 of the AI Act sets transparency obligations according to the role of the provider or deployer and the specific use. It does not require a cryptographic credential and it is not automatically satisfied by a seal. A verifiable identity complements the notices where those apply. See the official text and our guide for companies.
Argos is the first, not the only one planned. The rest of our superagents will join the same scheme, and each issuance will appear in the public registry. The inventory logic behind it is the same one we explain in the agent registry.
Frequently asked questions
Can Argos write to me without anyone reviewing it?
Its reference credential forbids outreach.send. The verifier checks that declaration; to confirm how a specific commercial channel operates you have to review and test its integration.
What is credential CRD-2026-0001?
It is the identifier of the credential issued to Argos on 8 September 2026. It contains the agent's DID, the issuer, the declared scope, the autonomy level, the manifest hash and the validity dates, and it is signed with ES256.
How do I know the credential is still valid today?
By opening the public verifier. Check the date, the status and the refresh policy of the response. An old image does not prove validity. The reference credential has a validity period of 90 days.
Could you change what Argos is forbidden to do without anyone noticing?
Altering the prohibitions inside the credential invalidates the signature. Changing permissions in an external system is not detected automatically: that requires change control, an operational check and a new issuance where appropriate.
What to do with this
- Check Argos yourself before reading any further on the subject. It takes less than a minute and it is the best way to understand the concept.
- Take the can / cannot table and write the equivalent for the most exposed agent in your company.
- Assign an autonomy level to each agent using an explicit scale, and check who approves external actions.
- Define which actions are forbidden to all of them, with no exceptions and no configurable override.
- Publish the list where a client can see it without asking permission.
If you want a read on which agents act on your behalf today and with what real scope: book your Digital Audit.
Editorial update of 17 September 2026, produced with the support of AI tools and cross-checked against public documentation. It is not presented as an external audit.
Identity and execution: the scope of this explainer
The public checks describe the credential and its relationship with the registered manifest. They do not prove the authentication of whoever presents it, the state of each external permission, or that actions are actually blocked. See the published evidence and limits.